11 of 140 staff accounts can sign in to Microsoft 365 with a password only.
Two of them are in finance and can approve supplier payments. Fix: enforce MFA with a Conditional Access policy and keep one monitored emergency account.
IT Security Review · ACSC Essential Eight
Glen Pather checks your IT security controls against the Australian Cyber Security Centre's Essential Eight, rates each one, and gives your board a costed plan to close the gaps. Fixed fee. No software or managed services to sell you.
Free scoping call with Glen. You get a written fixed quote within two business days.
Glen has led technology work at
Who it's for
Schools, not-for-profits, professional firms and government suppliers usually call for one of these reasons.
They want to know about MFA, backups and admin access, and nobody can answer with evidence.
Government and enterprise buyers now ask suppliers for their maturity level before they sign.
The only answer has come from the IT provider who runs the systems. Directors want a second opinion.
A staff member clicked a phishing link, or an invoice was redirected. You need to know what else is exposed.
A baseline before handover shows what the old provider left behind and what the new one must fix.
Cyber risk is now a standing board item. Directors need a clear, independent record that they asked and acted.
What you get
Glen does the work himself. It is not handed to a junior consultant after the sale.
Fee quoted in writing after the call. No hourly add-ons.
What your board receives
Every finding names the evidence, the fix and the cost. Directors get the summary. Your IT team gets the detail.
Two of them are in finance and can approve supplier payments. Fix: enforce MFA with a Conditional Access policy and keep one monitored emergency account.
One phishing email to any of them gives an attacker control of the whole tenant. Fix: create separate admin accounts and remove standing admin rights.
Fix: restore one server and one mailbox each quarter and record the result in the board risk report.
How it runs
Day 0
30 minutes with Glen. He asks about your systems, provider and deadlines, then sends a fixed quote.
Week 1
Glen meets your IT lead, your IT provider and finance, and collects read-only exports.
Week 2
Each control is tested against the ACSC maturity criteria. Findings are ranked and costed.
Week 3
Management sees the findings first. Then Glen presents the paper to your board or committee.
Month 6
A half-day follow-up re-rates what you've fixed and updates the board.
Who does the review
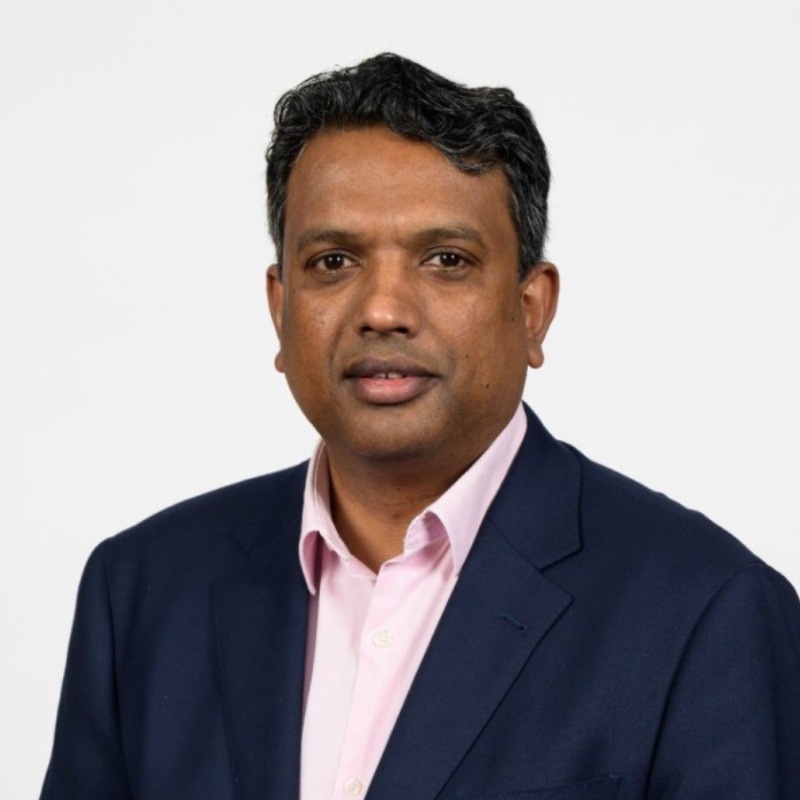
He started as an IT manager in 1995 and ran infrastructure for a group of BHP Billiton mines. Since then he has led IT strategy at Macquarie University, a cyber security uplift to Essential Eight Level 1, and technology programs in higher education, pharmaceuticals and federal government. He chairs the Council of The Scots College and sits on the board of East West Capital.
From people who've worked with Glen
Glen is a clear thinking leader. He quickly understands the big picture and will integrate the small detail where needed.
I have had the privilege of working closely with Glen for several years on the Scots College Council. He has always displayed the utmost professionalism and integrity.
Questions
Anything else, ask on the call.
A fixed fee, quoted in writing within two business days of the scoping call. It depends on staff numbers, sites and how many systems are in scope. There are no hourly charges on top.
Glen works with them, not around them. They see the findings before your board does and get a chance to respond. Most providers use the roadmap to justify work they have been recommending for a while.
No. Glen uses read-only admin access and exports from Microsoft 365 or Google Workspace, device management and your backup system. It is a controls review. If you also need a penetration test, he will scope it and refer a tester he trusts.
It depends on your contracts, your insurer and what you hold. Many mid-sized organisations reach Level 1 within 12 months and then work towards Level 2. The review recommends a target and explains why.
neopath does not resell software, licences or managed services. The roadmap is written for your own team or provider to deliver. Some clients ask Glen to oversee the remediation as a fractional CIO, but that is a separate decision.
No. Interviews run on Teams or Zoom. Glen presents to Sydney boards in person and to everyone else by video.
Free · 30 minutes · with Glen
Bring your IT lead or provider if you like. You'll leave with something useful whether or not you go ahead.